Complete technical information, architectural breakdown, and defensive guide
In the ever-evolving landscape of mobile cybersecurity, tools like Spyroid Rat V7.7 stand out as powerful remote access solutions for Android devices. Whether you’re a security researcher, ethical hacker, or simply curious about Android RATs (Remote Access Trojans), this comprehensive review dives into the features, interface, and capabilities of Spyroid Rat V7.7. Built with stealth and control in mind, this tool offers extensive monitoring and management options, making it a notable player in the realm of Android remote administration tools.
Spyroid Rat V7.7 is an advanced Android RAT designed for remote control and surveillance of Android devices. Promoted on platforms like GitHub and hacking forums, it’s marketed as a fully undetectable (FUD) tool that bypasses modern Android security features, including permission restrictions and background process limits. This version enhances previous iterations with improved evasion techniques, such as multi-layer droppers and integration with legitimate apps.
At its core, Spyroid Rat allows users to build, inject, and manage payloads for stealthy device access. It’s particularly noted for its web-based interface, persistence mechanisms, and comprehensive surveillance features. While often discussed in cybersecurity contexts for threat analysis, it’s important to note that such tools can pose significant risks to privacy and security if misused.
Based on the latest updates and interface screenshots, Spyroid Rat V7.7 packs a robust set of features tailored for remote monitoring and control. Here’s a breakdown of its standout capabilities:
The Builder module is the heart of Spyroid Rat V7.7, allowing users to create custom APK payloads. Key elements include:
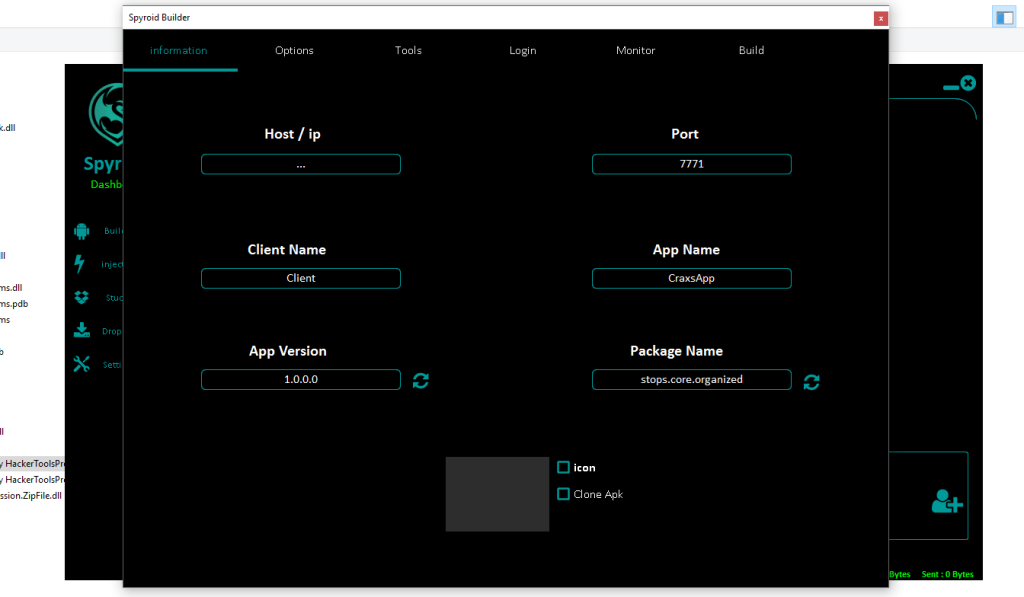
These options ensure the payload can evade detection on various Android ROMs, including MIUI and EMUI, by bypassing battery optimizations and autostart restrictions.
The Injector interface simplifies payload deployment:
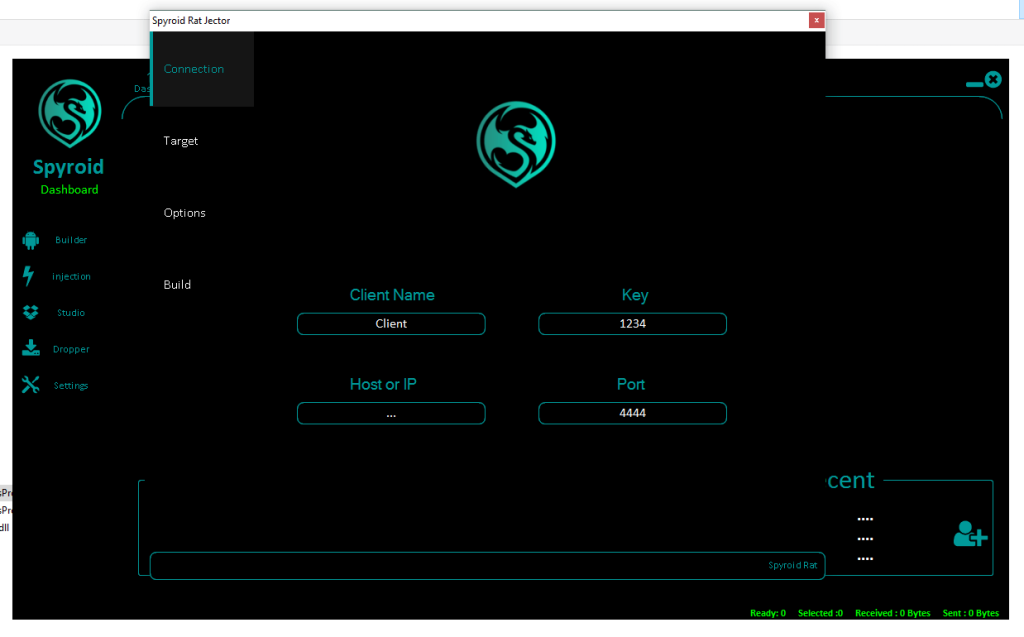
This module is designed for injecting the RAT into target devices, enabling persistent remote access.
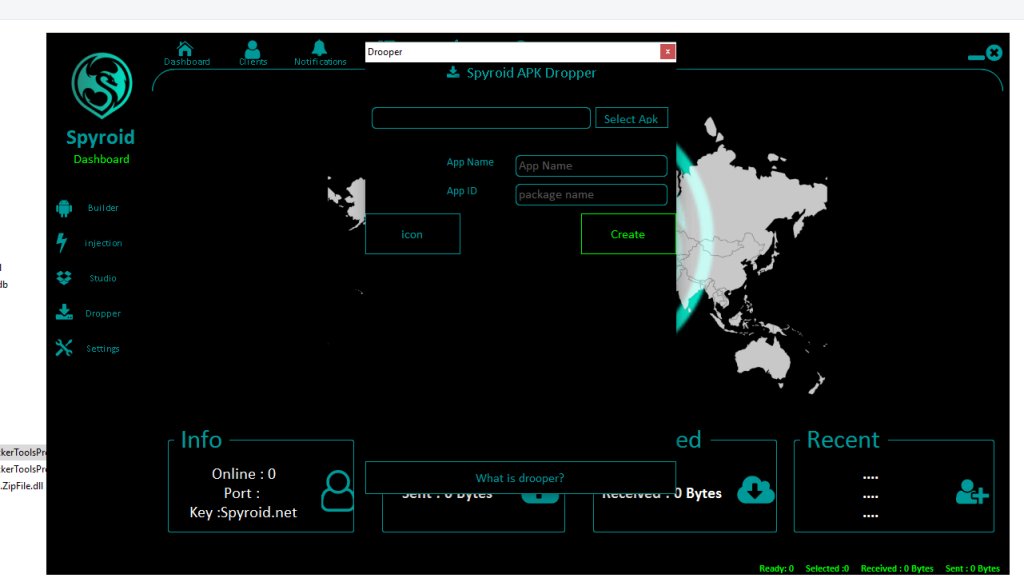
Spyroid Rat V7.7 includes an APK Dropper for distributing payloads:
The dropper uses cloud icons for upload/download visuals, emphasizing ease of deployment.
The main Dashboard provides a global overview:
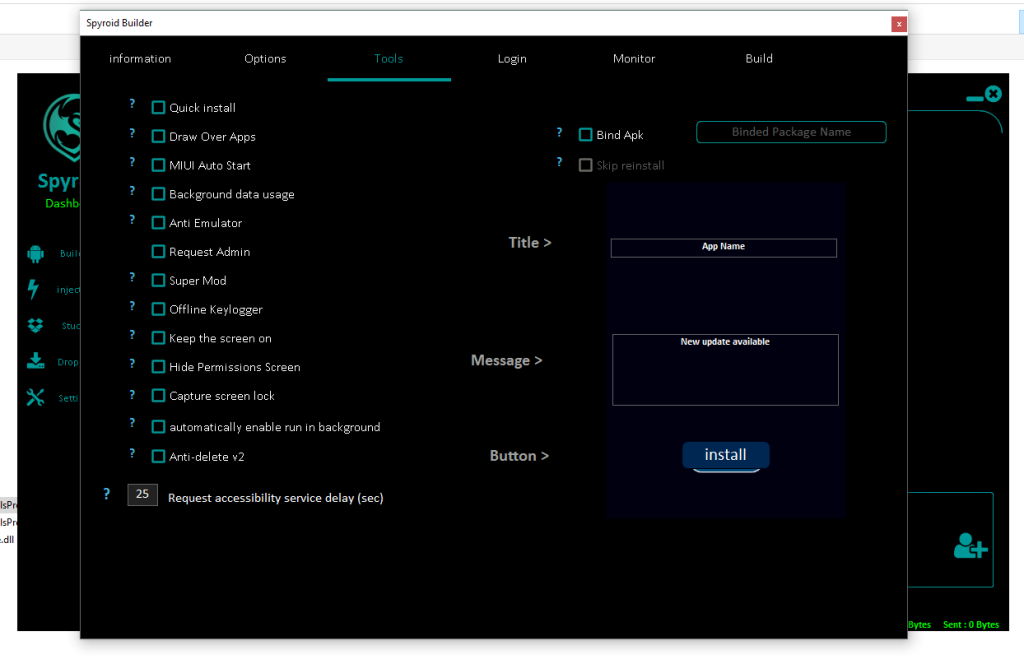
This interface resembles a command-and-control (C&C) panel, allowing real-time monitoring of infected devices.
Drawing from its core RAT functionality, Spyroid Rat V7.7 excels in stealthy operations:
These features make it a significant threat for Android privacy, as it can operate undetected while providing full device control.
Spyroid Rat V7.7 operates through a client-server model. Users build a custom APK using the Builder, inject it via the Injector or Dropper, and monitor via the Dashboard. Once installed on a target Android device, the RAT requests necessary permissions (often hidden), establishes a persistent connection, and relays data back to the controller.
Its FUD status comes from advanced evasion: anti-emulator checks prevent detection in virtual environments, anti-delete mechanisms resist uninstallation, and integration with real apps masks its presence. However, cybersecurity experts warn that tools like this can be flagged by antivirus software and Google Play Protect if not configured carefully.
As an Android RAT, Spyroid Rat V7.7 highlights vulnerabilities in mobile ecosystems. It can be used for legitimate purposes like parental control or device management, but its stealth features make it ideal for malicious activities such as data theft, espionage, or fraud. Recent reports link similar RATs to banking scams and privacy breaches, underscoring the need for robust Android security practices like regular updates, app vetting, and antivirus tools.
This website is dedicated to cybersecurity education, research, and authorized security testing. Any tutorials, demonstrations, malware analyses, or security tools presented are intended solely to help students, security professionals, and researchers understand cyber threats and improve defensive security practices.
All testing should be performed only in environments that you own or where you have explicit written authorization from the system owner.
The website owner is not responsible for any misuse of the information, software, or techniques described on this website. By using this website, you agree that you are solely responsible for your actions and compliance with all applicable laws.